PassMark OSForensics Free Download – Features, Benefits, and Installation Guide
Introduction
Digital evidence plays an important role in cybersecurity investigations, IT troubleshooting, incident response, and computer forensics. When suspicious activity occurs on a computer, investigators may need to examine files, search system data, review metadata, and identify artifacts that help explain what happened. Specialized forensic software can make these tasks more organized and efficient.
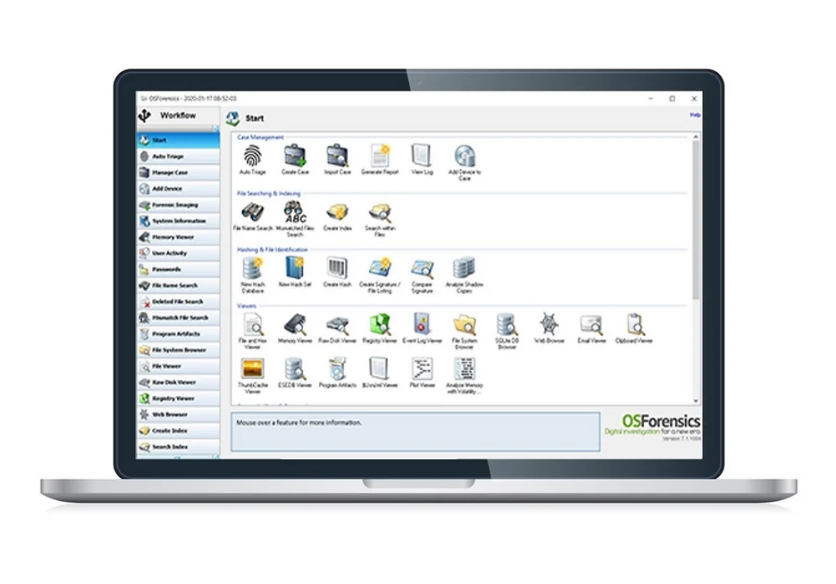
PassMark OSForensics is a computer forensics application developed by PassMark Software. It is designed to help users investigate digital information on Windows-based systems through a range of search, analysis, and evidence-examination tools.
If you are searching for a PassMark OSForensics free download, this guide explains the software's purpose, key features, potential uses, system requirements to check, and general installation process. It also covers licensing considerations and responsible evidence-handling practices.
Before downloading, remember that a free download does not necessarily mean every feature is available without a paid license. Always verify the current edition and licensing terms through the official publisher.
What Is PassMark OSForensics?
PassMark OSForensics is a digital investigation tool intended to help users locate, examine, and organize information stored on computer systems. It can be useful in situations where investigators need to search for files, inspect system artifacts, examine file information, or document findings.
Unlike a basic file manager, forensic software is designed to support a more structured investigation process. Depending on the edition and available modules, OSForensics may provide tools for file searching, indexing, hash analysis, system artifact examination, and other forensic tasks.
The software may be relevant to cybersecurity professionals, IT administrators, digital forensic specialists, and investigators working with authorized data sources. Its usefulness depends on the type of evidence, the operating environment, and the specific capabilities included in the version being used.
It is important to distinguish forensic examination from ordinary computer maintenance. Investigations often require careful documentation and preservation of original evidence. Simply locating a file or viewing a timestamp does not, by itself, prove what happened or who performed an action.
Key Features of PassMark OSForensics
The following sections describe common digital-forensics tasks associated with this type of software. Exact tools and availability can vary by OSForensics version and license, so check the official feature list before choosing an edition.
1. File and Content Search
Searching for relevant information is often one of the first steps in a digital investigation. A forensic tool can help users locate files by name, location, or other supported criteria.
Content-search capabilities may also help identify documents containing specific words or phrases. This can be useful when investigating a large collection of files or looking for information connected to a particular incident.
For example, an authorized investigator examining a company workstation may need to locate documents related to a security incident. Search and indexing tools can help narrow the results and make subsequent review more manageable.
2. File System Examination
File system examination helps investigators understand how files and directories are organized on a storage device. Relevant information may include file names, paths, sizes, timestamps, and other available metadata.
These details can provide useful context during an investigation. However, timestamps and metadata should be interpreted carefully because they may be affected by copying, software activity, system-clock differences, or deliberate modification.
The results should be considered alongside other evidence rather than treated as definitive proof on their own.
3. Digital Evidence Collection and Organization
Forensic investigations can involve large amounts of information from computers, storage devices, and other authorized sources. Organizing the relevant material is essential for efficient review and clear reporting.
Depending on the available tools, OSForensics may help users organize examination tasks, locate relevant artifacts, and record findings. A structured workflow makes it easier to explain what was examined and how conclusions were reached.
Investigators should also maintain appropriate records of evidence acquisition, access, and handling. For formal investigations, chain-of-custody requirements may apply.
4. Hashing and File Verification
Cryptographic hashes are values calculated from file contents. They can help investigators identify files and check whether data has changed between two points in a workflow.
When the same hashing algorithm is applied to identical file contents, the resulting hash should match. A changed file will generally produce a different hash value, although a hash alone does not establish when or why a change occurred.
Hashing is useful for verifying forensic copies, comparing files, and supporting evidence-integrity procedures. Investigators should record the algorithm used and follow an appropriate evidence-handling process.
5. Deleted File Investigation
Deleted data can sometimes remain recoverable on a storage device, depending on how deletion occurred and what happened afterward. Forensic and recovery tools may help identify remnants of deleted files or locate recoverable information.
Successful recovery is not guaranteed. Results depend on factors such as file-system behavior, storage technology, encryption, subsequent writes, and the condition of the device.
If a device contains important evidence, avoid unnecessary use because additional activity may overwrite recoverable data. For significant cases, qualified forensic personnel should determine the appropriate acquisition and examination procedure.
6. Windows Registry and System Artifact Analysis
Windows systems maintain various records and configuration data that may be relevant to a forensic investigation. These can include registry information, application-related artifacts, and other system records.
Where supported, OSForensics tools can help investigators examine relevant artifacts to better understand a system's configuration or activity.
Such artifacts require careful interpretation. Their presence does not automatically establish intent, user identity, or a complete sequence of events. A sound investigation compares multiple sources and documents uncertainties.
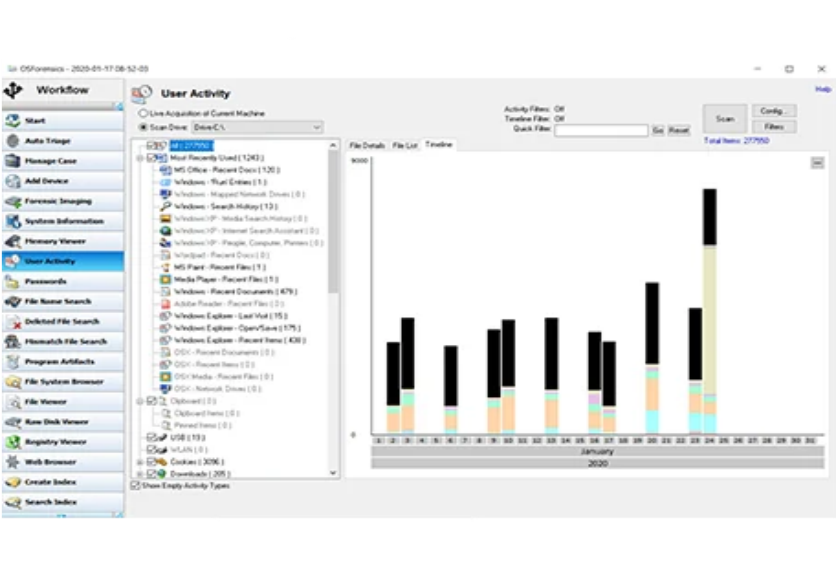
7. Timeline and Activity Analysis
Building a timeline can help investigators organize events using available timestamps and system records. A timeline may assist in identifying patterns, comparing activity across sources, and deciding which evidence requires further review.
However, timestamps can be affected by time zones, clock settings, copying, synchronization, and application behavior. Investigators should confirm the meaning of each timestamp before drawing conclusions.
The availability and scope of timeline-related tools should be verified for the particular OSForensics edition.
8. Indexing and Reporting
Indexing can make large collections of files easier to search by preparing information for faster retrieval. It may reduce the need to repeat the same search operations during an investigation.
Reporting tools, where included, can help summarize findings and organize relevant information for review. Clear reports should distinguish observed facts from interpretations and conclusions.
For professional investigations, retain the necessary supporting records so that another qualified person can understand and verify the examination process.
Benefits of Using PassMark OSForensics
OSForensics can help users manage complex digital investigations through a combination of search, analysis, and reporting capabilities.
Faster data discovery: Search and indexing tools can help locate relevant files in large data collections.
Evidence identification: Hash matching and drive-signature analysis can help identify known files and investigate suspicious data.
Centralized case management: Case and reporting tools help organize findings and supporting information.
Deleted-data examination: Supported tools can assist with identifying or recovering certain deleted files.
System activity analysis: Relevant artifacts and timestamps can help investigators develop a clearer understanding of computer activity.
Flexible investigation workflows: The software provides tools for different stages of digital examination.
Digital investigation+1
These capabilities can save time, but they do not eliminate the need for technical knowledge, evidence validation, or careful documentation.
Who Should Use PassMark OSForensics?
OSForensics is primarily intended for users who need to investigate computer data rather than simply manage everyday files.
Digital forensic investigators: Examine computer systems and organize evidence for investigations.
Cybersecurity professionals: Investigate suspicious files, potential compromises, and other security incidents.
IT administrators: Review system information and investigate unusual activity on authorized devices.
Incident-response teams: Collect and analyze relevant information following a security event.
Security researchers: Examine files and system artifacts in controlled, authorized environments.
Forensics students: Learn digital investigation techniques using appropriate training systems and sample data.
Beginners can learn the software, but users conducting formal investigations should understand evidence preservation, data integrity, and the limitations of forensic findings.
PassMark OSForensics Free Download Options
PassMark provides an official download page for OSForensics. The publisher currently lists OSForensics version 11.1, build 1017, and offers a free trial option through its product listings. Availability, trial restrictions, and licensing conditions should be checked before installation.
Download+1
You can visit the official OSForensics download page to review the available installer and supported versions.
Before downloading, consider the following:
Confirm that you are downloading OSForensics from PassMark's official website.
Check the current version and its compatibility with your Windows system.
Review the free-trial conditions and determine which features are available.
Compare the subscription and perpetual-license options if you need continued professional use.
Read the licensing terms before using the software for commercial or organizational investigations.
A trial is useful for evaluating the interface and determining whether the software meets your needs. However, trial access should not be confused with a permanent, unrestricted free license.
Avoid cracked versions and modified installers. Such files can contain malware, interfere with forensic work, or compromise the integrity of an investigation.
PassMark OSForensics System Requirements
The official download page lists the following compatibility and hardware information for OSForensics. Requirements can change with later releases, so check the publisher's documentation before installing.
Download
Requirement | Officially listed information |
|---|---|
Operating systems | Windows 7, 8, 10, and 11 |
Windows Server | Server 2012, 2016, 2019, and 2022 |
Architecture | 64-bit support; 32-bit deprecated |
Minimum RAM | 2 GB |
Recommended RAM | 16 GB or more |
Free storage | 500 MB, or operation from a USB drive as supported |
For larger investigations, additional RAM and storage may be beneficial, particularly when indexing many files or working with substantial evidence collections.
Also consider the storage space required for forensic images, case data, temporary files, and exported reports. If you intend to investigate external drives or disk images, verify that your system and chosen workflow support the relevant source format.
How to Download and Install PassMark OSForensics
Follow these general steps to install the software.
Step 1: Open the Official Website
Visit the OSForensics download page. Confirm that the website and product name match the software you want.
Step 2: Review the Available Version
Check the current release, supported operating systems, and licensing options. The publisher also provides older versions for users who need them, although it recommends upgrading where possible.
Download
Step 3: Download the Installer
Download the installation file directly from the official source. Avoid unofficial repackaged installers and websites that require unnecessary download managers.
Step 4: Verify the Download
Check the file's publisher information and scan it with reputable security software before running it. For forensic environments, follow your organization's approved software-validation procedures.
Step 5: Run the Setup Program
Open the installer and follow the on-screen instructions. Review the license terms and select the appropriate installation options.
Step 6: Launch OSForensics
Open the program and familiarize yourself with its main workspace, search tools, analysis modules, and case-management features.
Step 7: Start With a Test Dataset
Before examining important evidence, practice with sample files or a test system that you are authorized to use. This helps you understand the workflow without unnecessarily changing or risking original data.
How to Use PassMark OSForensics
The exact workflow depends on the investigation, the available modules, and the edition of the software. The following steps provide a general starting point.
Define the investigation: Record the purpose of the examination and identify the data source you are authorized to inspect.
Prepare the evidence: Follow suitable acquisition and preservation procedures before examining a device that may contain important evidence.
Create or organize a case: Use the available case-management features to keep examination details and findings organized.
Search relevant data: Use supported file-search and indexing functions to locate information related to the investigation.
Examine artifacts: Review relevant metadata, file information, system records, or other supported evidence sources.
Validate findings: Compare relevant results and consider alternative explanations before drawing conclusions.
Document the process: Record the methods used, relevant observations, limitations, and any supporting evidence.
Prepare a report: Use available reporting tools to summarize findings for appropriate review.
PassMark provides official support resources and tutorials to help users understand the software's features and workflows.
Support
Digital Forensics and Responsible Use
Digital forensic software can access sensitive information, so responsible use is essential. Before examining a computer, confirm that you have permission and a legitimate reason to access the data.
For investigations where evidence integrity matters, consider these practices:
Preserve the original evidence whenever possible.
Use appropriate write-protection and acquisition procedures.
Record when and how evidence was collected.
Maintain chain-of-custody documentation when required.
Record relevant hashes and verification results.
Protect confidential information and restrict access to authorized personnel.
Follow applicable laws, organizational policies, and investigation procedures.
Avoid treating a single file, timestamp, or search result as conclusive proof. Strong forensic conclusions require context, corroboration, and a clear record of the methods used.
Pros and Cons of PassMark OSForensics
Pros
Designed specifically for computer forensic investigation.
Offers file searching and indexing capabilities.
Supports hash matching and evidence identification.
Includes case-management and reporting features.
Provides documentation, tutorials, and support resources.
Offers a trial option for evaluating the software.
Diagnostic and test software for computers+1
Cons
Some features may require a paid license.
Advanced investigations can require specialized technical knowledge.
Large evidence collections may need substantial memory and storage.
Deleted-file recovery is not guaranteed.
Findings must be interpreted carefully and validated.
Compatibility and feature availability depend on the release and edition.
OSForensics is most useful when its investigation capabilities match the task at hand and the user follows an appropriate evidence-handling process.
Best Alternatives to PassMark OSForensics
If you are comparing forensic applications, the following tools are worth considering.
Autopsy
Autopsy is a digital forensics platform built around The Sleuth Kit. It provides a graphical interface for examining disk images and investigating digital evidence. It may suit users looking for an open-source forensic workflow.
The Sleuth Kit
The Sleuth Kit is a collection of command-line tools and libraries for examining disk images and file-system data. It is particularly useful for technically experienced users who want a flexible, tool-based workflow.
Magnet AXIOM
Magnet AXIOM is a commercial digital investigation platform designed to collect and examine evidence from supported sources. Check the vendor's current capabilities, licensing, and system requirements before selecting it.
X-Ways Forensics
X-Ways Forensics is a commercial forensic examination tool used for detailed analysis of storage media and digital evidence. It may appeal to experienced investigators seeking specialized forensic functionality.
Belkasoft Evidence Center
Belkasoft Evidence Center is a commercial digital forensics and incident-response product. Review its supported evidence sources, licensing, and capabilities to determine whether it fits your needs.
The best choice depends on your budget, experience, evidence sources, reporting requirements, and the operating systems you need to examine.
Frequently Asked Questions
Is PassMark OSForensics free to download?
PassMark provides a download and trial option. The trial's limitations and the features included in each license should be confirmed on the official website. Downloading the installer does not automatically provide a permanent full license.
Is PassMark OSForensics compatible with Windows 11?
The official download page lists Windows 11 among the supported operating systems. Always check the current requirements for the exact version you plan to install.
Download
Can OSForensics recover deleted files?
The software advertises deleted-file investigation and recovery capabilities. Success depends on the storage device, file system, data condition, and whether deleted information has been overwritten. Recovery is not guaranteed.
Digital investigation
Can OSForensics help investigate suspicious computer activity?
Yes. Its advertised capabilities include searching and indexing, hash matching, drive-signature analysis, and tools for organizing forensic findings. These can help investigators examine suspicious data, but the results still require validation and context.
Diagnostic and test software for computers
Is OSForensics suitable for beginners?
Beginners can learn the interface and practice with sample datasets. However, users working with real evidence should understand forensic principles, data integrity, and the importance of documenting their actions.
Is PassMark OSForensics safe to download?
The recommended approach is to download it from PassMark's official website, verify the installer, and follow your organization's software-security procedures.
Does OSForensics offer a paid version?
Yes. PassMark lists trial and purchase options, with licensing choices described in its official product information. Check the current terms to compare the available licenses.
Diagnostic and test software for computers+1
Conclusion
PassMark OSForensics is a digital investigation application designed to help users discover, identify, examine, and organize computer-based evidence. Its search and indexing functions, hash matching, artifact analysis, and case-reporting capabilities can support a range of authorized forensic and cybersecurity workflows.
If you are looking for a PassMark OSForensics free download, begin with the official download page, review the trial and licensing terms, and verify that your computer meets the system requirements. Practice with sample data before working on important evidence, and follow suitable preservation and documentation procedures.
Choosing the right edition and using it responsibly can help make digital investigations more organized, repeatable, and easier to document.